Unit 42 Finds 13,229 Malicious URLs In AI Phantom-Domain Study
Palo Alto Networks’ Unit 42 said its phantom-squatting research generated 685,339 prompts across 913 brands and produced 2.1 million unique URLs, including 13,229 malicious URLs and about 250,000 unique phantom domains. The public report did not disclose the brand list, affected customer names or named domains tied to data loss.
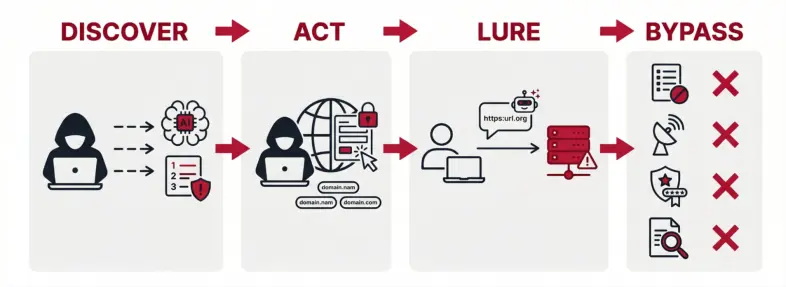
Palo Alto Networks’ Unit 42 maps AI-hallucinated domains
Palo Alto Networks’ Unit 42 described phantom squatting as a security problem created when large language models generate plausible but nonexistent domains.
The research team said attackers can register those domains before a user, developer or AI agent follows the model’s recommendation.
The findings have not been independently replicated.
Victim organizations or customers affected by a specific domain remain outside the public record.
The research framed the risk around trusted AI output.
A coding assistant could invent a benefits portal, a research agent could suggest a fake banking portal, or a developer could place an AI-generated API endpoint into code that later sends data to attacker-controlled infrastructure.
Unit 42 outlines four phases in the attack lifecycle
The research divides the phantom-squatting lifecycle into four phases: discover, act, lure and bypass.
Attackers first probe a target brand’s hallucination surface by asking models realistic questions that may produce fictitious URLs.
The act phase begins when attackers register the most useful hallucinated domains.
The team said generic top-level domains can be registered quickly and cheaply, and observed domains moved from initial registration to malicious content within hours.
The lure phase uses the model itself as the delivery channel.
A user or autonomous AI agent receives a confident recommendation from a sanctioned assistant and visits infrastructure controlled by an attacker, without a traditional phishing email or advertisement.
Newly registered domains can evade reputation-based defenses
The researchers said conventional URL defenses often depend on prior reputation, threat-intelligence history or blocklist entries.
Newly registered hallucinated domains can begin with none of those signals.
The report said some attackers can extend that clean-window advantage through redirect cloaking, benign content for automated crawlers and CAPTCHA-protected infrastructure.
Those techniques make a newly registered domain harder to classify before a user or agent reaches it.
Unit 42 says testing covered 913 brands and 2.1 million URLs
Unit 42 said its methodology generated 685,339 prompts across 913 global brands in technology, finance, healthcare, e-commerce, government, gambling and logistics.
The URL-generation phase used two model families, labeled LLM1 and LLM2, across three temperature settings.
The pipeline produced 2.1 million unique URLs.
Unit 42 said threat-intelligence systems flagged 13,229 of those URLs, or 0.61%, as malicious at the time of analysis.
Unit 42 said it categorized another 41,313 URLs, or 1.90%, as high risk.
The company also said 809,455 generated URLs, or 37.28%, resolved to nonexistent domains.
Unit 42 said that after normalization, those fictitious endpoints collapsed into approximately 250,000 unique phantom domains.
The remaining public-record gaps are the brand list, affected customer names, registered malicious domain names, remediation outcomes, and public evidence that any named organization lost data through phantom squatting.