SendTech Times
News
MARKET SIGNAL:

IBM, Red Hat And Deloitte Put Lightwell On Regulated Open-Source Patch Work

Newsroom brief

Deloitte is joining IBM and Red Hat’s Lightwell initiative to map open-source components, validate patches and support regulated software supply chains, backed by IBM and Red Hat’s $5 billion commitment.
Verified against source materialEdited by SendTech Times Cybersecurity DeskSource: SiliconANGLE
IBM, Red Hat And Deloitte Put Lightwell On Regulated Open-Source Patch Work
Image source: SiliconANGLE

Deloitte Joins IBM And Red Hat’s Lightwell Work

Deloitte is joining IBM and Red Hat’s Lightwell initiative, adding consulting and forward-deployed engineering support to an open-source security program aimed at regulated software supply chains.

IBM and Red Hat said they launched Lightwell in May with a $5 billion initial commitment and 20,000 engineers assigned to the effort.

The program is designed to help enterprises detect and patch vulnerabilities in the open-source projects that sit inside their software.

Deloitte’s role is operational.

The company will work with IBM to help joint customers map the open-source components their developers use, then keep that inventory current as software changes.

The purpose is to reduce the risk that a company misses a vulnerable module inside an application.

The partnership gives Lightwell a services layer.

IBM and Red Hat provide automated patch validation, while Deloitte manages patch installation and checks whether the fixes work in customer environments.

Regulated Software Supply Chains Are The Target

IBM, Red Hat and Deloitte said the partnership will focus on regulated software supply chains.

That points the work toward organizations where software security must also satisfy sector-specific cybersecurity rules.

Deloitte brings a large cybersecurity services business to the partnership.

SiliconANGLE reported that Deloitte had $70.5 billion in revenue as of fiscal 2025 and helps enterprises scan infrastructure for vulnerabilities, detect breaches and handle related security tasks.

The consulting firm gives IBM and Red Hat access to teams that already work with enterprise security programs.

Regulated customers have to fit open-source remediation into audit, reporting and maintenance processes, not only developer workflows.

The companies also plan to support breach reporting to regulators.

They will notify open-source maintainers about vulnerabilities before public disclosure, giving project teams time to prepare patches before attackers learn the details.

The patch process is not always simple.

A security update may require the latest version of a project or extensive configuration changes.

Lightwell is being framed as a way to test whether fixes work before they are pushed into regulated enterprise systems.

That division of labor is specific: Deloitte handles installation and effectiveness validation, while IBM and Red Hat supply the automated patch-validation layer.

The companies are trying to turn open-source vulnerability response from a case-by-case engineering scramble into a maintained component inventory and remediation workflow.

Forward-Deployed Engineers Add Customer-Site Support

Deloitte will assign forward-deployed engineers to support the effort.

These developers work at client organizations and will help with vulnerability remediation and ongoing software maintenance.

Their presence also gives customers a named team for follow-up maintenance after a patch is applied.

Savio Rodrigues, IBM’s vice president of service partners, said Lightwell was created to address open-source software security in an AI-driven threat landscape.

He said the effort combines engineering, automation and ecosystem partnerships to tackle the risk at scale.

IBM, Red Hat and Deloitte have described the Lightwell structure, commitment and engineering model, but they have not disclosed named customers, remediation volumes or measured patch-time reductions.

Share this article
inXf

Related articles

More
Cybersecurity buyers use 39 September deals to fill AI and OT gaps
Cybersecurity

Cybersecurity buyers use 39 September deals to fill AI and OT gaps

SecurityWeek counted 39 cybersecurity M&A deals in September, with buyers using acquisitions to add OT visibility, AI-security controls, offensive-testing scale, sovereign-technology work and compliance reach.

AI Patch Study Keeps Humans In Vulnerability Reviews
Cybersecurity

AI Patch Study Keeps Humans In Vulnerability Reviews

The Register reported that 1Password Off-by-1 Labs tested 6,080 AI-generated patches across six CVEs and found clean autonomous fixes in 26.0 percent of cases, leaving security teams with a supervision problem rather than a replacement for vulnerability review.

Defcon Badge Makes Open Security Chip Inspectable As Hardware Token
Cybersecurity

Defcon Badge Makes Open Security Chip Inspectable As Hardware Token

WIRED via Ars Technica reported that Defcon's 2026 badge uses Andrew Huang's Baochip-1x, a mostly open source microcontroller with a removable module that works as a hardware security token and exposes the silicon for infrared inspection.

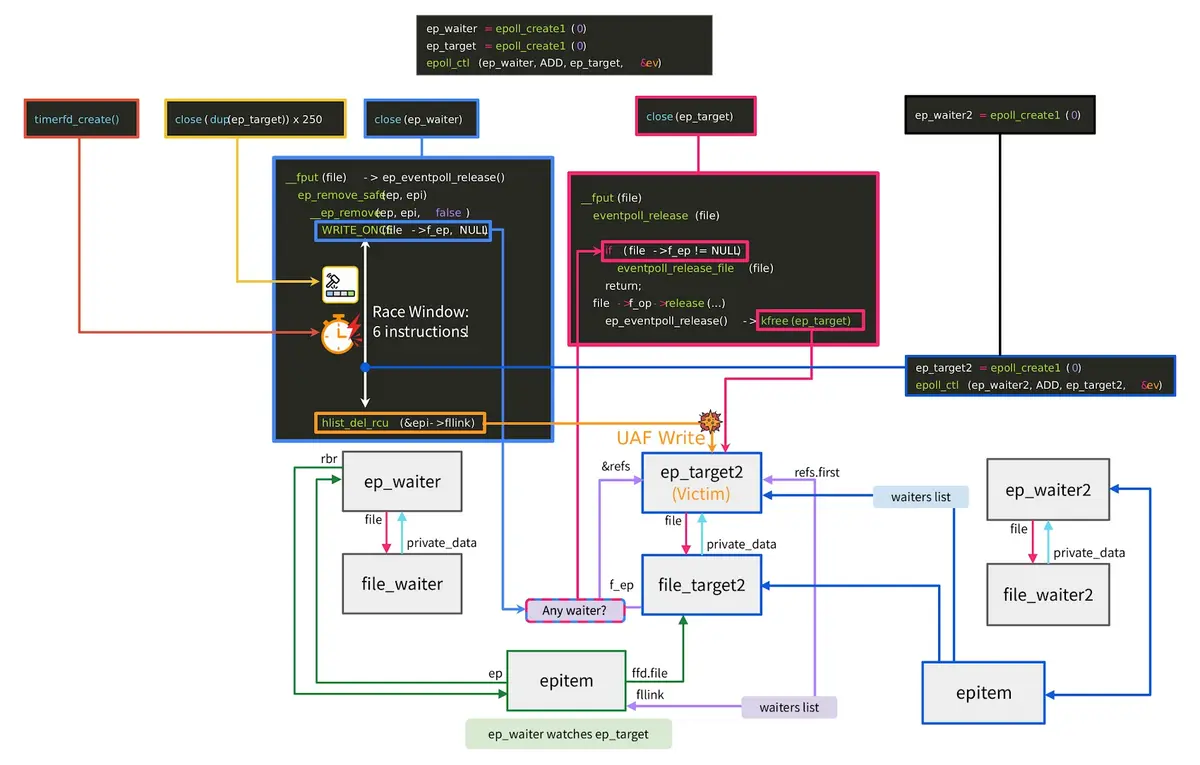
Bad Epoll Linux Flaw Reaches Android Without A Public Patch Timetable
Cybersecurity

Bad Epoll Linux Flaw Reaches Android Without A Public Patch Timetable

A newly disclosed Linux kernel flaw tracked as CVE-2026-46242 can let an unprivileged local user gain root access on Linux systems and may be reachable from Android or Chrome sandbox contexts, but public material did not give a distribution-by-distribution patch timetable.

EU Cyber Resilience Act Puts 24-Hour Clock On Software Supply Chains
Cybersecurity

EU Cyber Resilience Act Puts 24-Hour Clock On Software Supply Chains

The European Commission lists 11 September 2026 as the start of Cyber Resilience Act reporting duties and 11 December 2027 for its main product-security obligations. Manufacturers face distinct reporting and engineering deadlines.

CISA Android and Linux Warnings Put Patch Timing Back on the Security Agenda
Cybersecurity

CISA Android and Linux Warnings Put Patch Timing Back on the Security Agenda

CISA added exploited Android and Linux vulnerabilities to its Known Exploited Vulnerabilities catalog. The Android flaw affects Android 14 through 16, while the Linux issue centers on older kernel branches and cgroups v1 container environments. The immediate test is whether agencies and infrastructure operators apply vendor updates or mitigations by CISA's June 5 deadline.

Cisco Unified CM Flaw Puts WebDialer Exposure Under Patch Pressure
Cybersecurity

Cisco Unified CM Flaw Puts WebDialer Exposure Under Patch Pressure

Cisco disclosed fixed-release guidance for a critical Unified Communications Manager flaw that can let attackers gain root privileges when WebDialer is enabled. Cisco PSIRT is aware of public proof-of-concept exploit code for CVE-2026-20230, though it has not found active exploitation or targeting. The immediate test is whether administrators patch Unified CM or disable WebDialer before proof-of-concept code turns into wider exposure.

CISA WebLogic Warning Turns Oracle Patch Lag Into an Exposure Test
Cybersecurity

CISA WebLogic Warning Turns Oracle Patch Lag Into an Exposure Test

CISA ordered U.S. federal agencies to patch Oracle WebLogic Server systems affected by CVE-2024-21182 after active exploitation was observed. Shodan tracks more than 1,592 exposed WebLogic servers vulnerable to the flaw, including 961 on version 12.2.1.4.0 and 631 on version 14.1.1.0.0. The immediate test is whether public- and private-sector defenders apply Oracle fixes or remove exposed systems where mitigations are unavailable.

Keep Reading

More Stories

Latest
Anthropic Program Pairs Claude With Infrastructure Security TeamsAIOct 10, 2026Anthropic Program Pairs Claude With Infrastructure Security TeamsAnthropic is pairing Claude models, its engineers and outside cybersecurity firms to scan critical infrastructure and open-source software for vulnerabilities, with an opt-in service for maintainers.ABC Shareholders Seek Board Seats After South Africa Market SanctionsPoliticsOct 10, 2026ABC Shareholders Seek Board Seats After South Africa Market SanctionsShareholders holding about 76% of Africa Bitcoin Corporation want a meeting to appoint two non-executive directors after South Africa's FSCA sanctioned three former Altvest executives.Morocco King Defends Spain Partnership After Ceuta Migrant RushPoliticsOct 10, 2026Morocco King Defends Spain Partnership After Ceuta Migrant RushKing Mohammed VI said Morocco’s partnership with Spain remains a sovereign choice after more than 70,000 migrants crossed into Ceuta, while promising partners a strategic vision for co-development and stability.Atlassian AMP Targets AI Code Attribution Across Enterprise WorkflowsAIOct 10, 2026Atlassian AMP Targets AI Code Attribution Across Enterprise WorkflowsAtlassian’s Agentic Multiplayer Protocol links agent identity, code attribution, Rovo Work oversight and EU-hosted inference controls to help enterprises track mixed human and AI software work.Unpatched AhsayCBS Flaws Used to Deploy Webshells and Crypto MinersCybersecurityOct 10, 2026Unpatched AhsayCBS Flaws Used to Deploy Webshells and Crypto MinersThreat actors are chaining two AhsayCBS vulnerabilities to bypass authentication, execute commands, install webshells and hide XMRig mining activity on backup management servers.Australian Security Teams Know Passkeys Are Safer, But Passwords Still DominateAIOct 10, 2026Australian Security Teams Know Passkeys Are Safer, But Passwords Still DominateYubico and Okta’s authentication survey found Australian technical teams recognise passkey security while legacy onboarding, fragmented MFA and AI phishing keep passwords embedded in enterprise access.Nasuni Adds Governed AI Access to File Data Platform After DryvIQ and Resilio DealsCloud & Data CentersOct 10, 2026Nasuni Adds Governed AI Access to File Data Platform After DryvIQ and Resilio DealsNasuni has folded DryvIQ governance and Resilio edge delivery into its file data platform, adding MCP-based AI access, enterprise search and a PSYCHIC framework for AI-ready data.Universal Quantum Raises $100 Million for Trapped-Ion Computing ExpansionChips & SemiconductorsOct 10, 2026Universal Quantum Raises $100 Million for Trapped-Ion Computing ExpansionUniversal Quantum raised more than $100 million in a Series A round to commercialise trapped-ion quantum products and expand in Singapore, the US, Japan and Germany.Neela Raises £2.1M To Pilot Waste-To-SAF BiotechEconomyOct 10, 2026Neela Raises £2.1M To Pilot Waste-To-SAF BiotechCambridge startup Neela Biotech raised £2.1m to move its AI-guided microbial waste-to-SAF process from lab work into pilot trials at an existing biogas plant over the next two years.India and Saudi Arabia Put Port Investment Talks on Strategic Maritime RouteEconomyOct 9, 2026India and Saudi Arabia Put Port Investment Talks on Strategic Maritime RouteIndia and Saudi Arabia discussed possible Saudi participation in Vadhavan and Galathea Bay port projects, linking Gulf trade, container transshipment and maritime capacity building.MIT Expands STEM Workforce Training Through AI And Design ProgramsAIOct 9, 2026MIT Expands STEM Workforce Training Through AI And Design ProgramsMIT for America will scale existing university education programs nationwide, combining calculus support, responsible AI resources and hands-on fabrication to address STEM workforce access gaps.Google Maps Expands Restaurant Search Into Food OrderingCapital & PolicyOct 9, 2026Google Maps Expands Restaurant Search Into Food OrderingGoogle Maps is adding more dining workflow features, with Gemini-powered Ask Maps ordering links through Toast, Square and Uber Eats plus city trend lists and practical restaurant review signals.